🔔 Release Announcement – SafeLine WAF v9.4.0
Published 25 days ago
# SafeLine WAF
Announcements
Published 25 days ago
Carrie-SafeLine
Admin
Updated 25 days ago
0
Semantic Analysis Engine Update
- Added detection for the Apache Kafka Connect arbitrary file read vulnerability (CVE-2025-27817).
- Added detection for multiple .NET deserialization attack vectors, covering Json.NET, FastJson, XML, NetDataContractSerializer, Xaml, BinaryFormatter, and more.
- Added detection for the DedeCMS 5.7.2 remote code injection vulnerability (CVE-2025-6335).
- Optimized detection logic for SQL injection, command injection, XSS, and CSRF.
- Optimized detection logic for Java deserialization, as well as Java, PHP, and ASP code injection.
- Optimized MongoDB NoSQL injection detection, covering Query parameters, Forms, and JSON Keys.
- Optimized bot detection and server response detection logic.
- Optimized Gzip decoding and HTTP protocol parsing for complex requests and compressed responses.
- Optimized enhanced rules: low-risk command execution, system file access, Maccms 8.x RCE (CVE-2017-17733), dangerous Python functions, and Java code injection.
Added
- Support for forwarding rule synchronization in master-slave deployment mode.
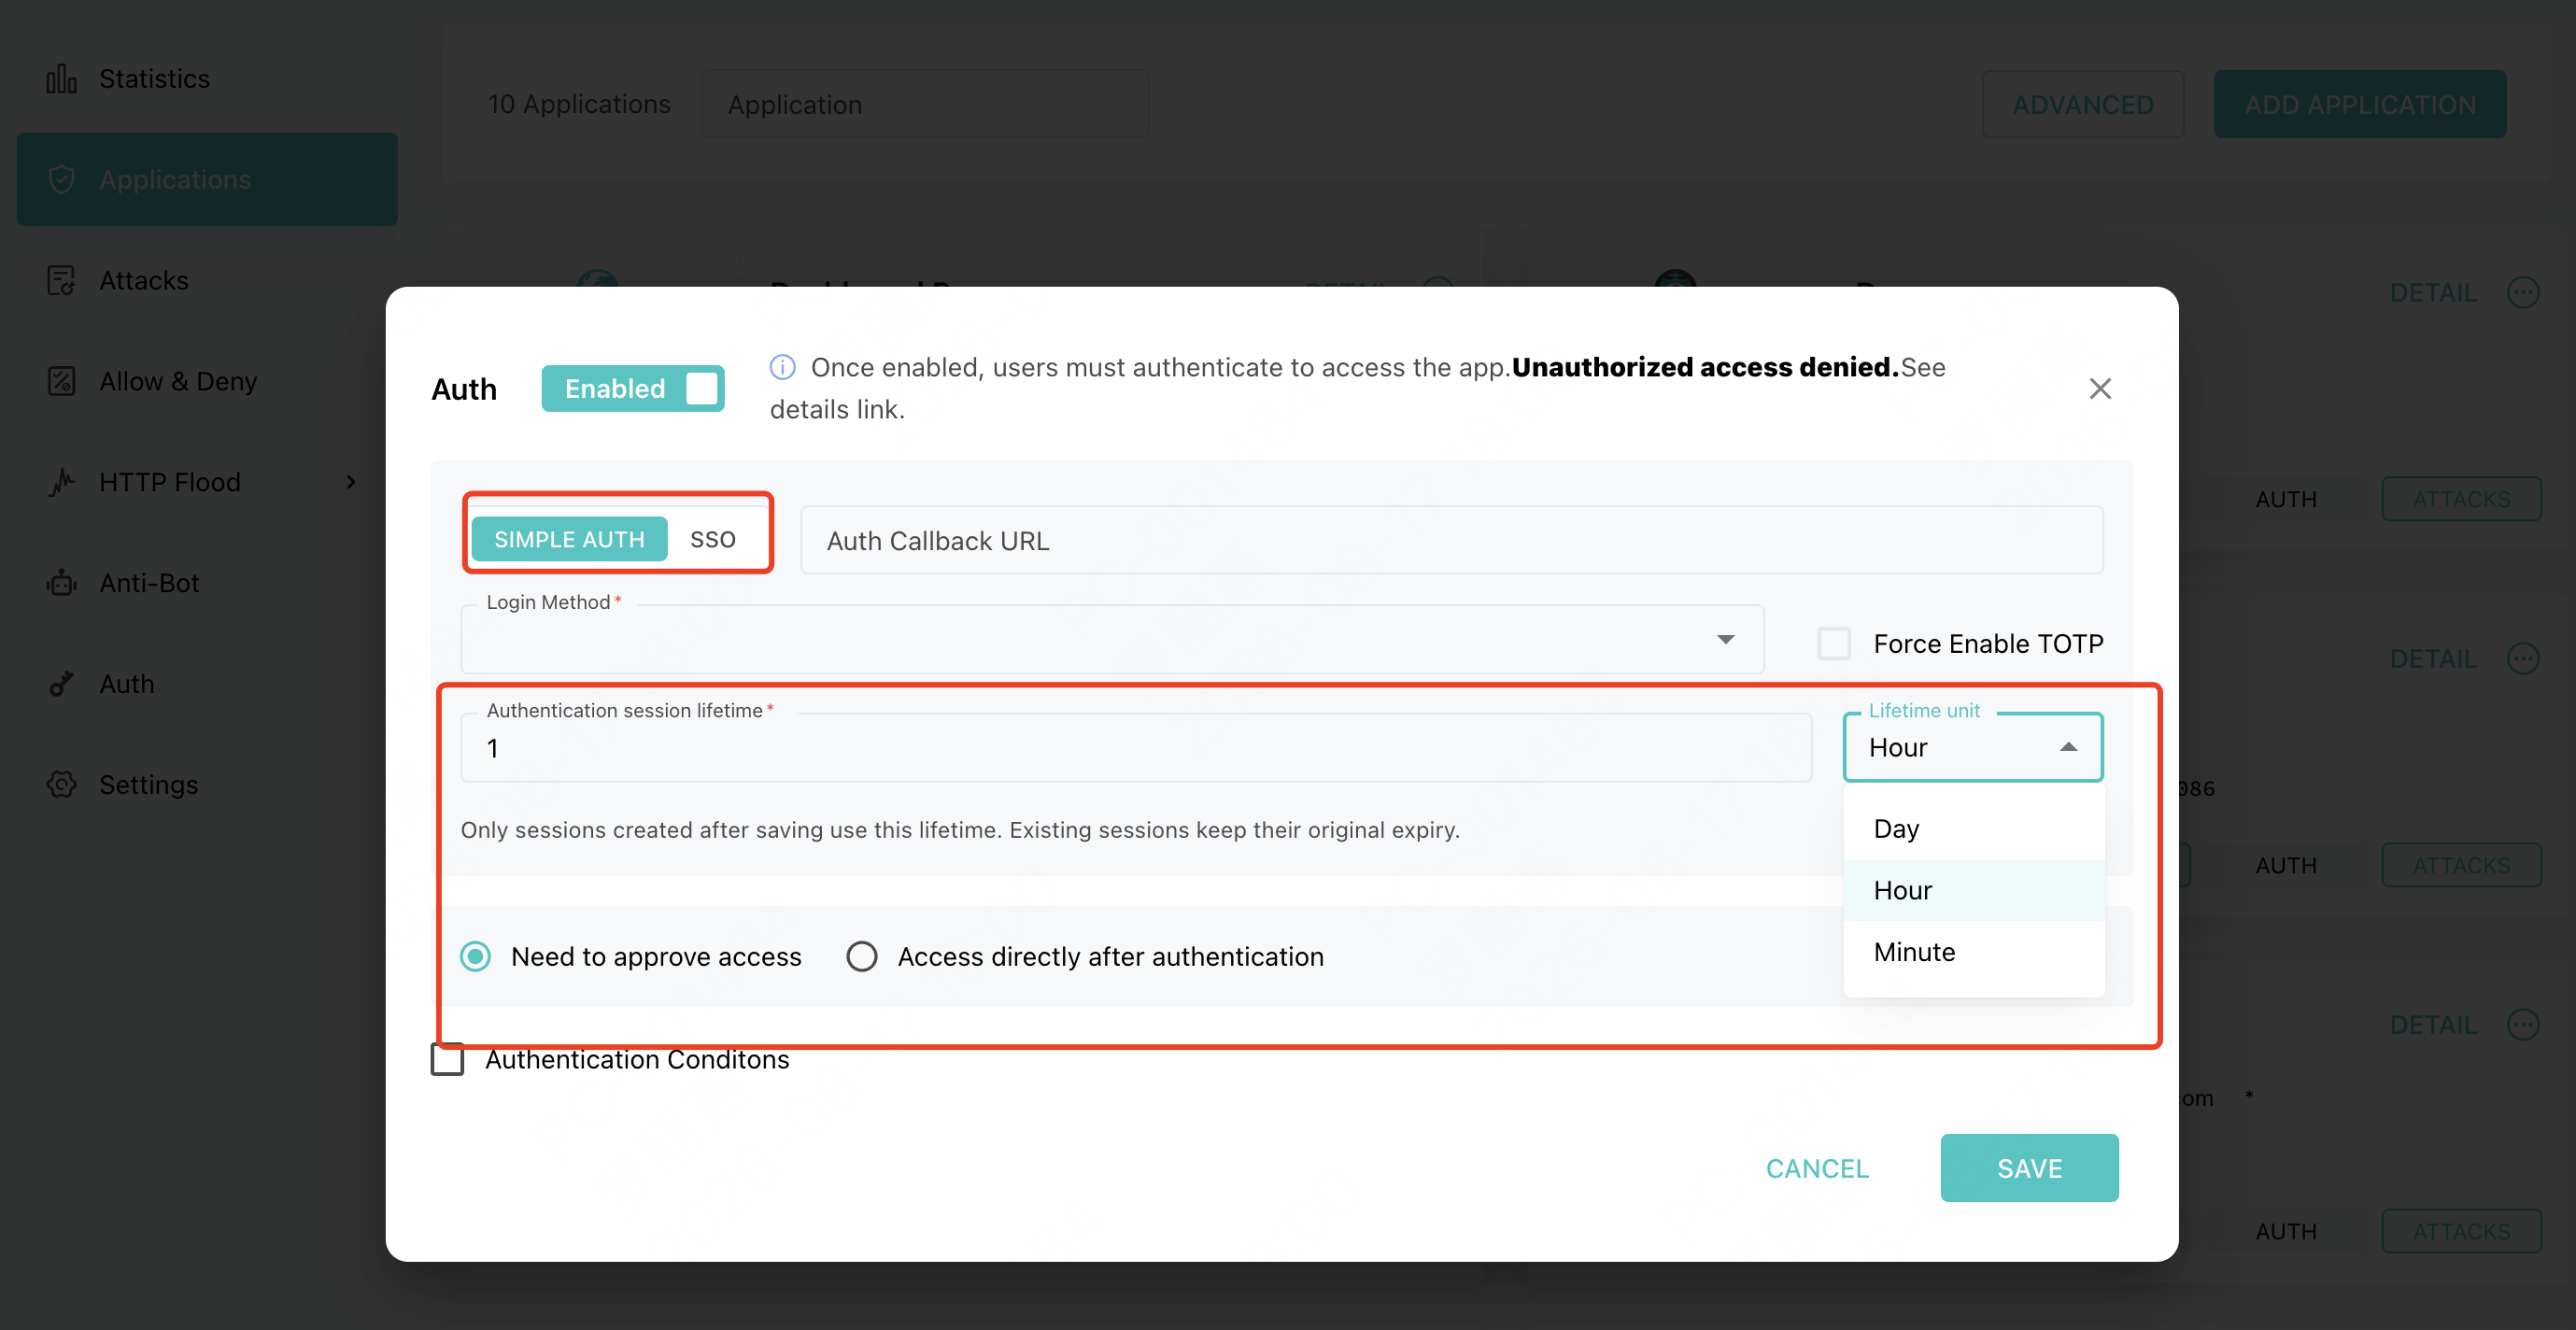
- Configuration for authentication session validity, available for both Simple Auth and Unified SSO.
Improvements
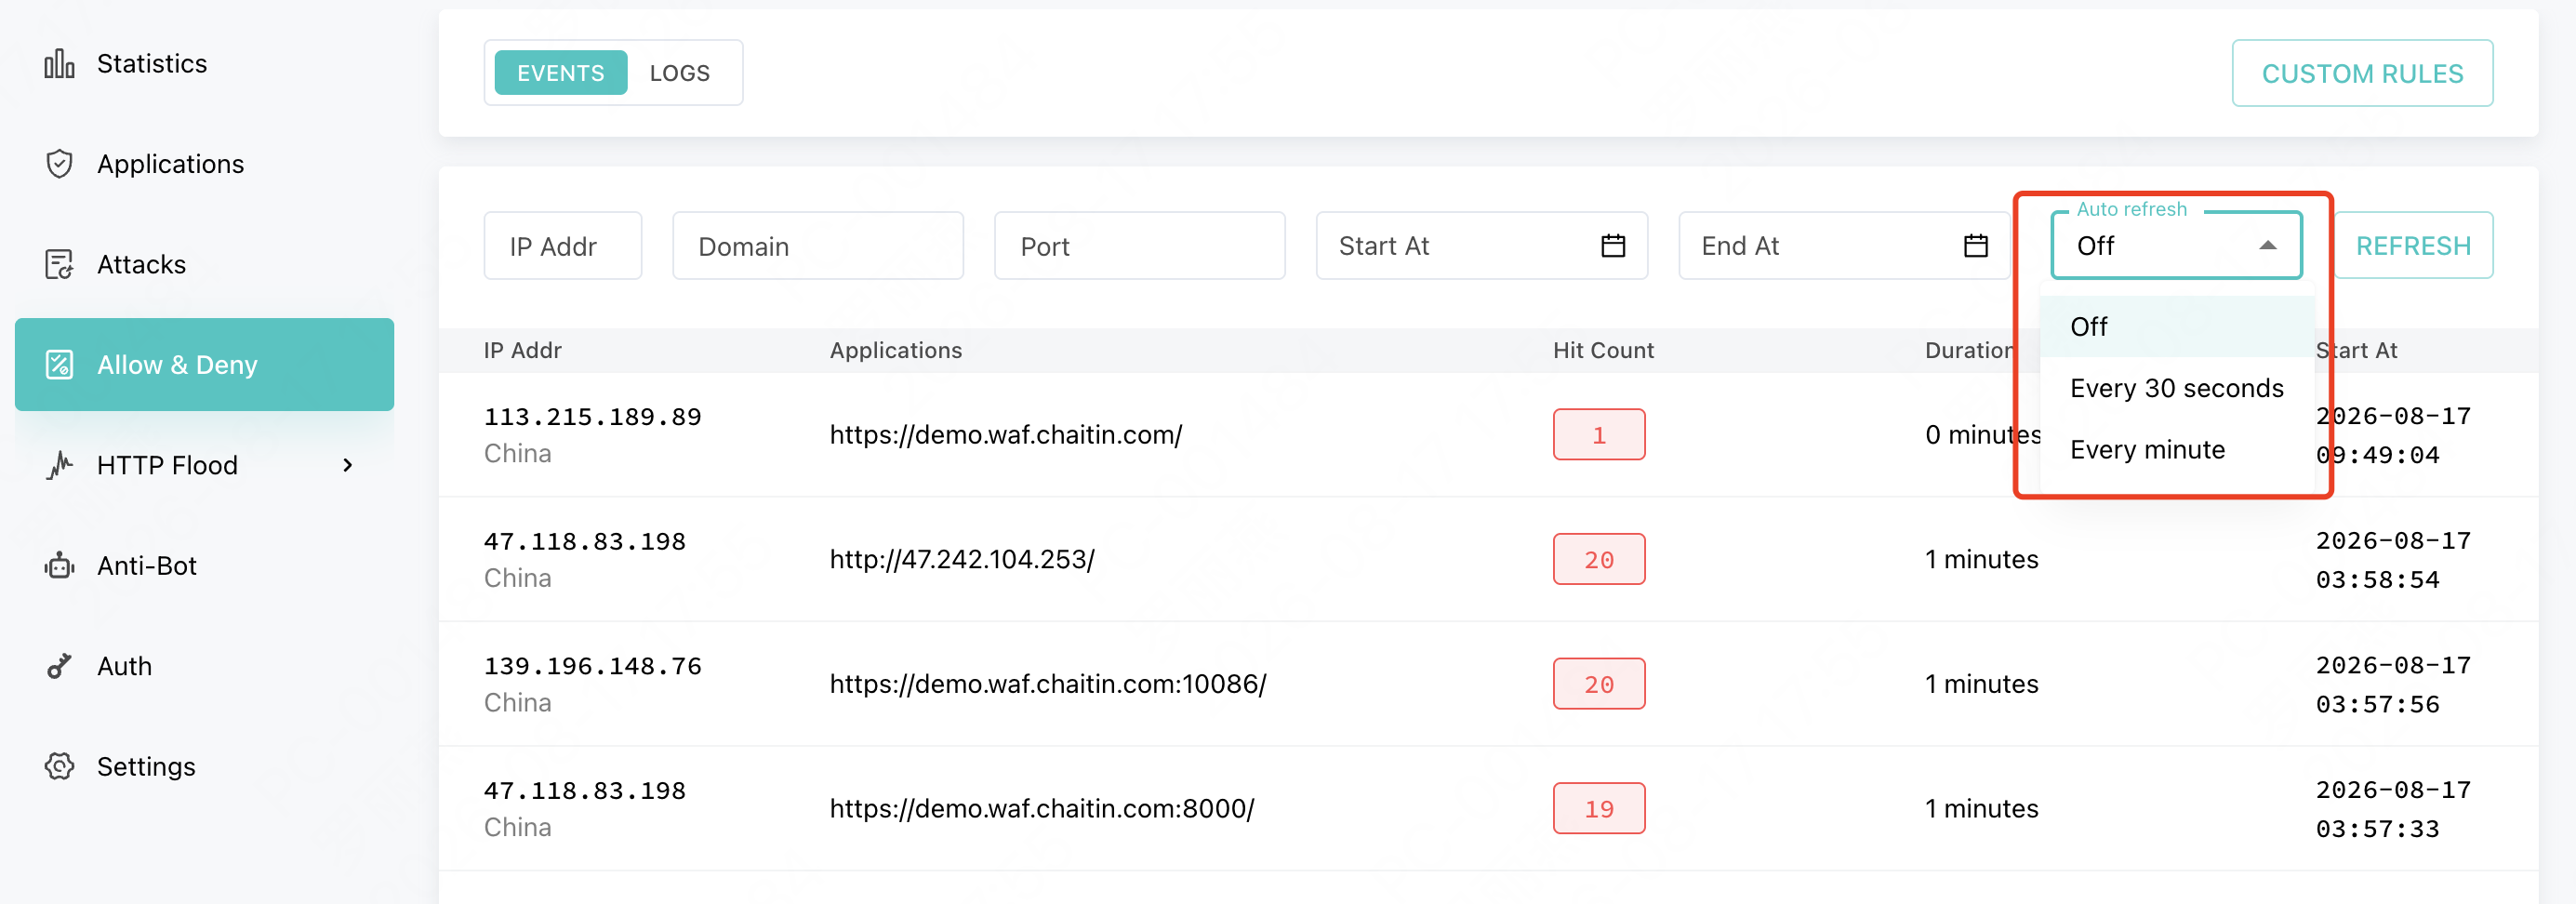
- Added automatic refresh for Attack Logs and Allowlist/Blocklist Detection Logs.
Bug Fixes
- Fixed an issue where the Secret appeared empty after configuring GitHub as an authentication source.
- Fixed an encoding issue in SSO when the business URL contained multiple, duplicate, or already-encoded parameters — the original business URL is now restored correctly after authentication.
- Corrected the Allow Rule "Today's Hits" link behavior — the log entry is now only available when "Continue detecting and logging attack requests for allowlisted traffic" is enabled.
- Fixed the "AbortError: The user aborted a request" error popup.
- Fixed Anti-bot Challenge slider compatibility on iPhone devices.
- Fixed a v9.3.11 upgrade issue where backfilling a large number of historical rule logs could time out and prevent safeline-mgt from starting.
Changelog & Upgrade Guide
- https://docs.waf.chaitin.com/en/Reference/Changelog
- https://docs.waf.chaitin.com/en/GetStarted/Upgrade
⚠️ Important Notice
If you are upgrading from v9.2.7 or earlier, please carefully review the v9.2.7 changelog and manually migrate the relevant Nginx configuration:
https://docs.waf.chaitin.com/en/Reference/Changelog#h-927-28-october-2025